
Create your first Agent
Configure a provider, connect a Tool, create an Agent, and run your first session.
Before you start
- A reachable control plane and a running Industric Operator (see Deploy & operate).
- Access to the Platform to configure your provider, Tool, and Agent.
- The
exoCLI installed for the optional CLI steps below. kubectlaccess only if you choose the YAML examples.
1. Set up the model provider
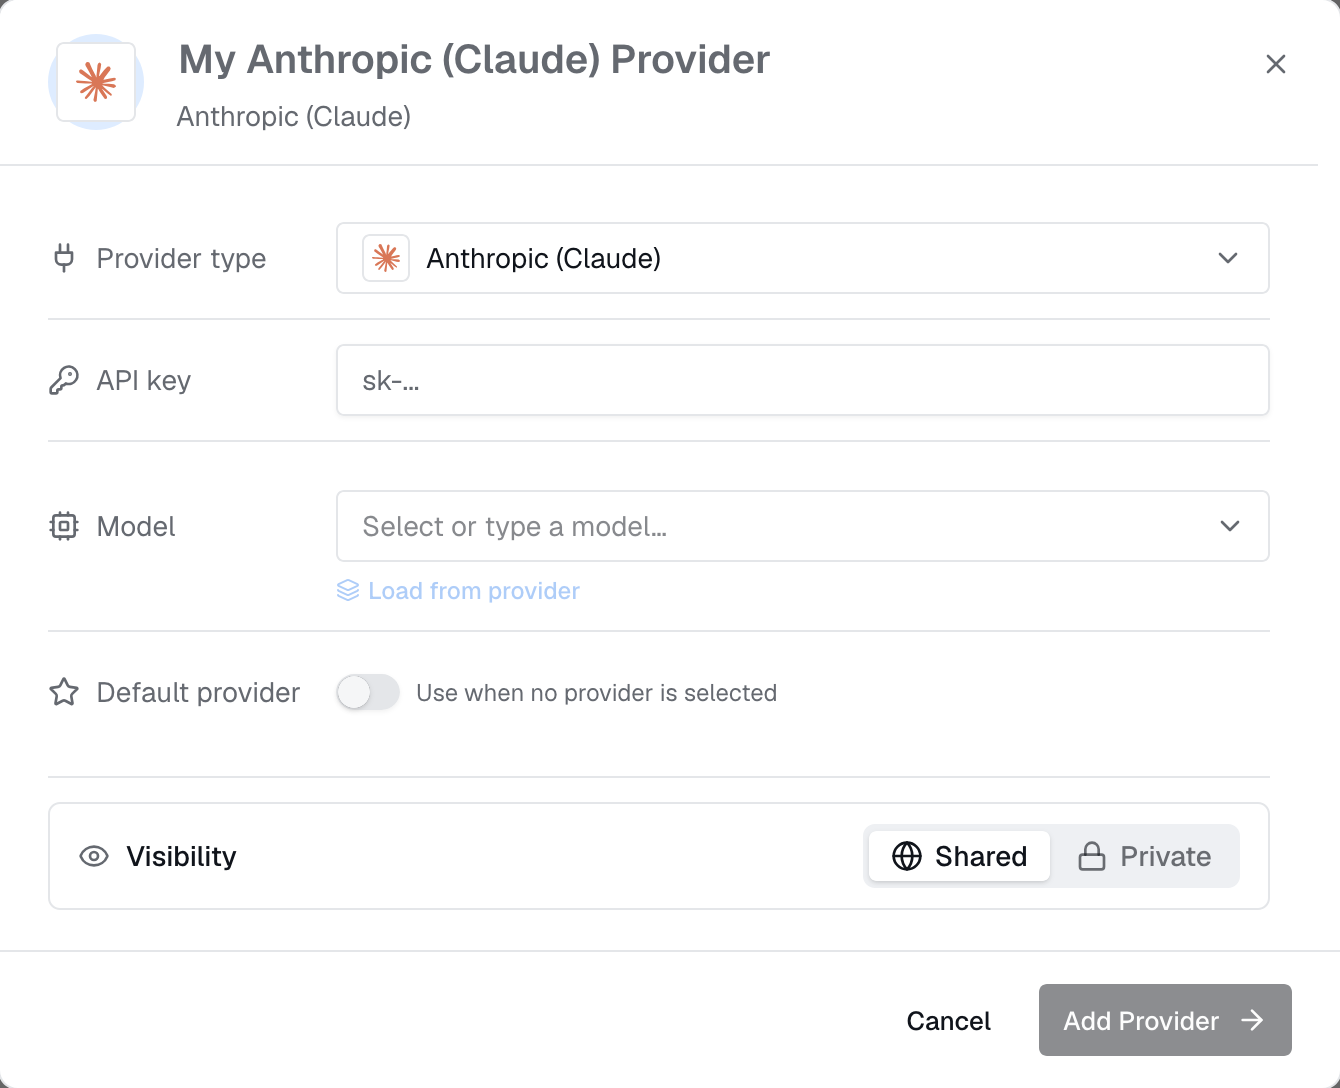
The Agent resolves its model credentials from a provider the platform holds, so configure that first. In the Platform, go to Connect → Providers → Add provider: pick Anthropic (Claude) for the ClaudeCode runtime used here, paste the API key, and tick Set as default provider. Validate checks the key before anything is saved.
2. Create a Tool
A Tool is a managed connection (a database, SSH host, HTTP endpoint, or Kubernetes cluster). The credential lives in a Secret and never leaves the cluster.
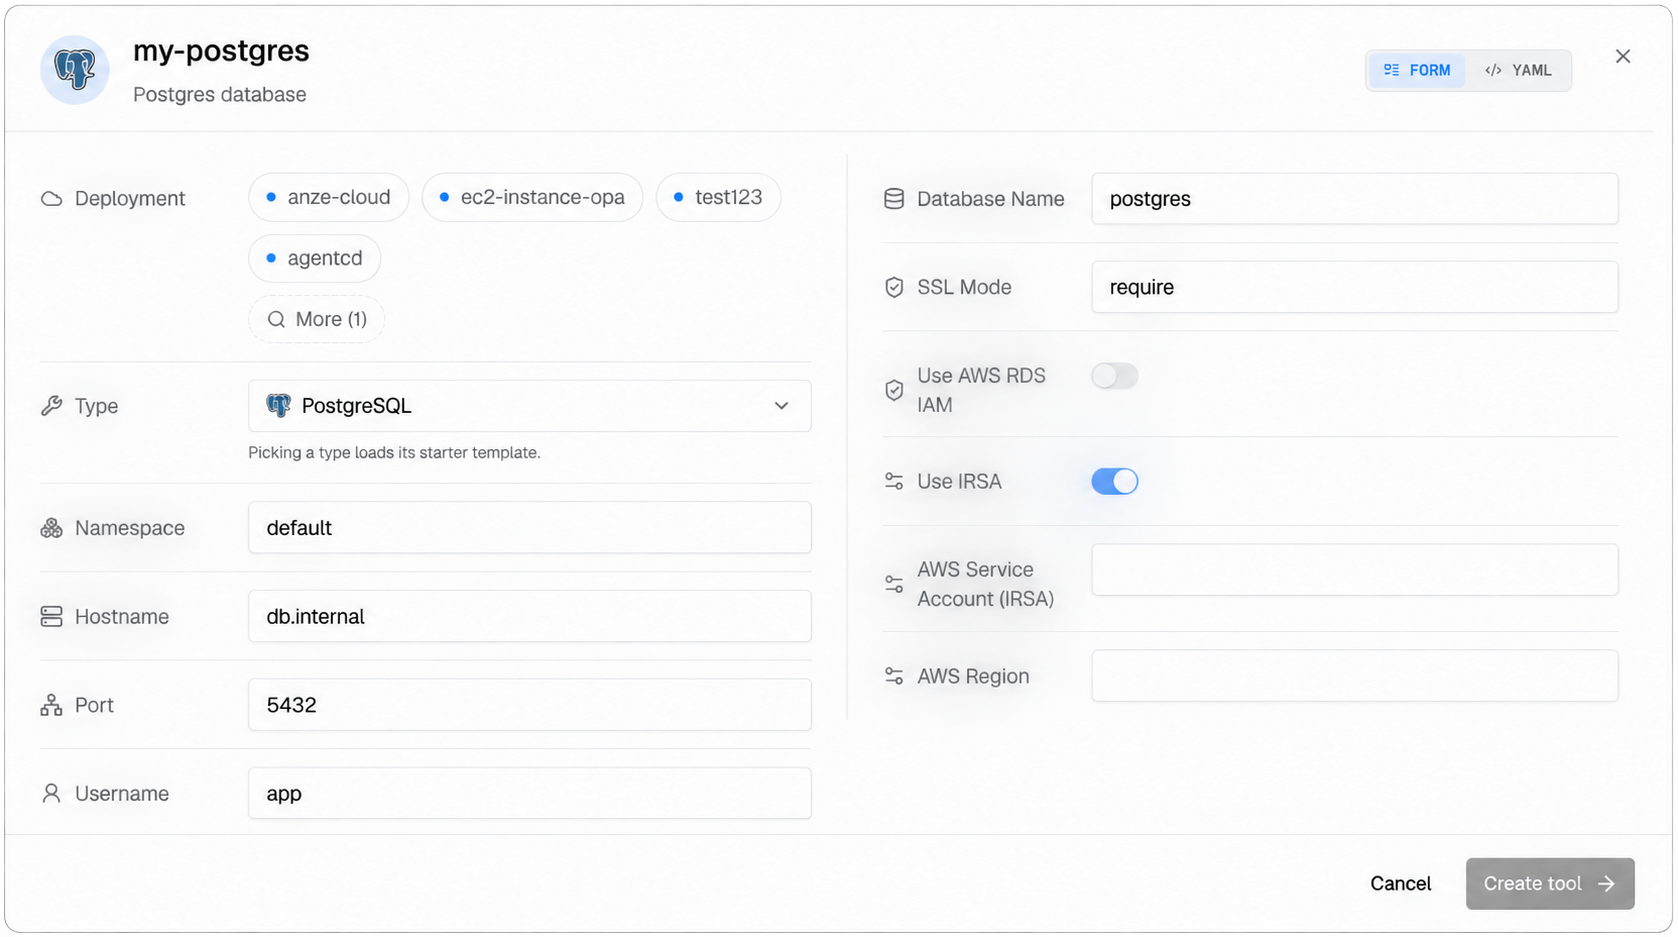
In the Platform, open Tools and create a tool. Select your deployment and PostgreSQL. Name it analytics-postgres in the adaptive namespace, enter the connection settings, then select Create tool.
Create with YAMLApply a Kubernetes manifest instead.
Alternatively, save this as first-tool.yaml:
1apiVersion: v12kind: Secret3metadata:4 name: analytics-pg-creds5 namespace: adaptive6type: Opaque7stringData:8 password: REPLACE_ME9---10apiVersion: autonomic.sh/v1alpha111kind: Tool12metadata:13 name: analytics-postgres14 namespace: adaptive15spec:16 type: postgres17 description: "Analytics Postgres read-replica"18 tags:19 - databases20 - postgres21 - readonly22 probe: true23 config:24 hostname: pg-analytics.prod.internal25 port: 543226 username: autonomic_ro27 databaseName: analytics28 sslMode: require29 credentialsRef:30 name: analytics-pg-creds31 key: passwordprobe: true the reconciler runs a connectivity check before marking the Tool Ready.Apply it and wait for the probe to pass. Ready means the reconciler reached the database with the credentials you gave it:
kubectl apply -f first-tool.yaml
kubectl -n adaptive get tools
3. Create the Agent
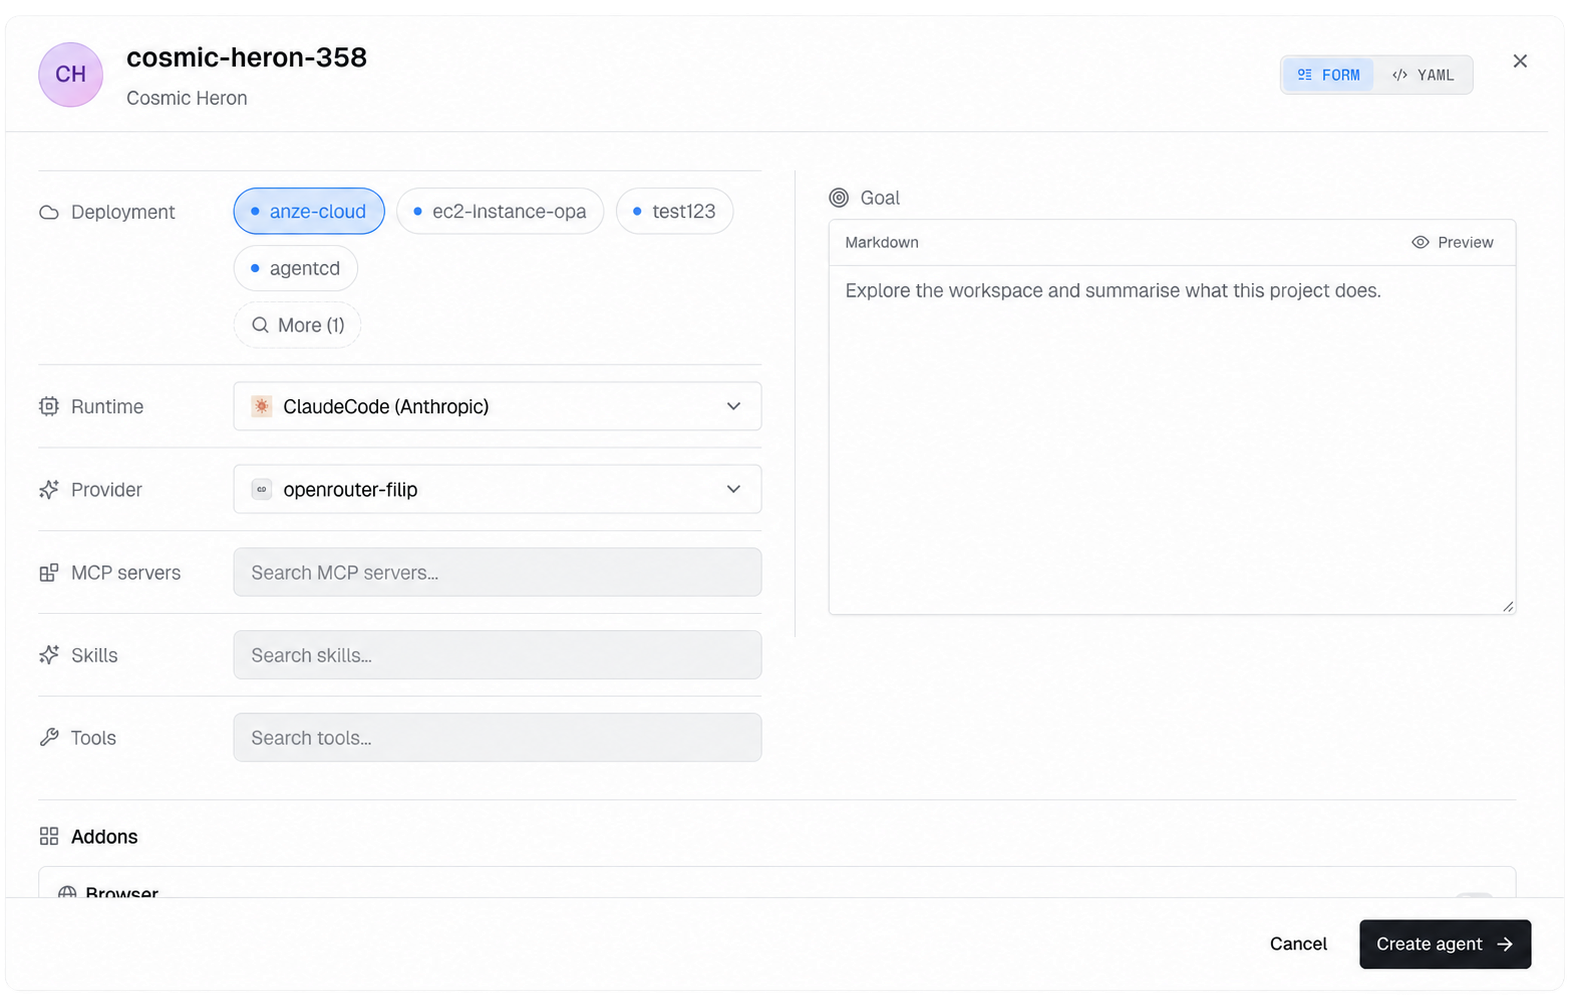
In the Platform, create an agent and select your deployment, runtime, and provider. Name it hello-agent in the adaptive namespace. Add the Tool from step 2 and set the goal to report the five most recent signups, then select Create agent.
Create with YAMLApply a Kubernetes manifest instead.
A minimal Agent declares a runtime, a goal, a provider, and the Tool it may call. Choose the model in the provider configuration. Save this as first-agent.yaml:
1apiVersion: autonomic.sh/v1alpha12kind: Agent3metadata:4 name: hello-agent5 namespace: adaptive6spec:7 runtime: ClaudeCode8 phase: Paused9 goal:10 inline: |11 Connect to the analytics database and report the 5 most recent signups.12 provider:13 type: claude14 bootstrap:15 skills:16 - analytics-postgresstatus.effectiveTools lists native runtime and MCP tools, not bootstrap tools or skills. exo agent get uses your platform login and does not need a kubeconfig.Apply it with kubectl:
kubectl apply -f first-agent.yaml
kubectl -n adaptive get agent hello-agent
phase: Paused so you can read the configuration before any run spends tokens. Opening a terminal activates the agent and starts its session.4. Connect to the agent
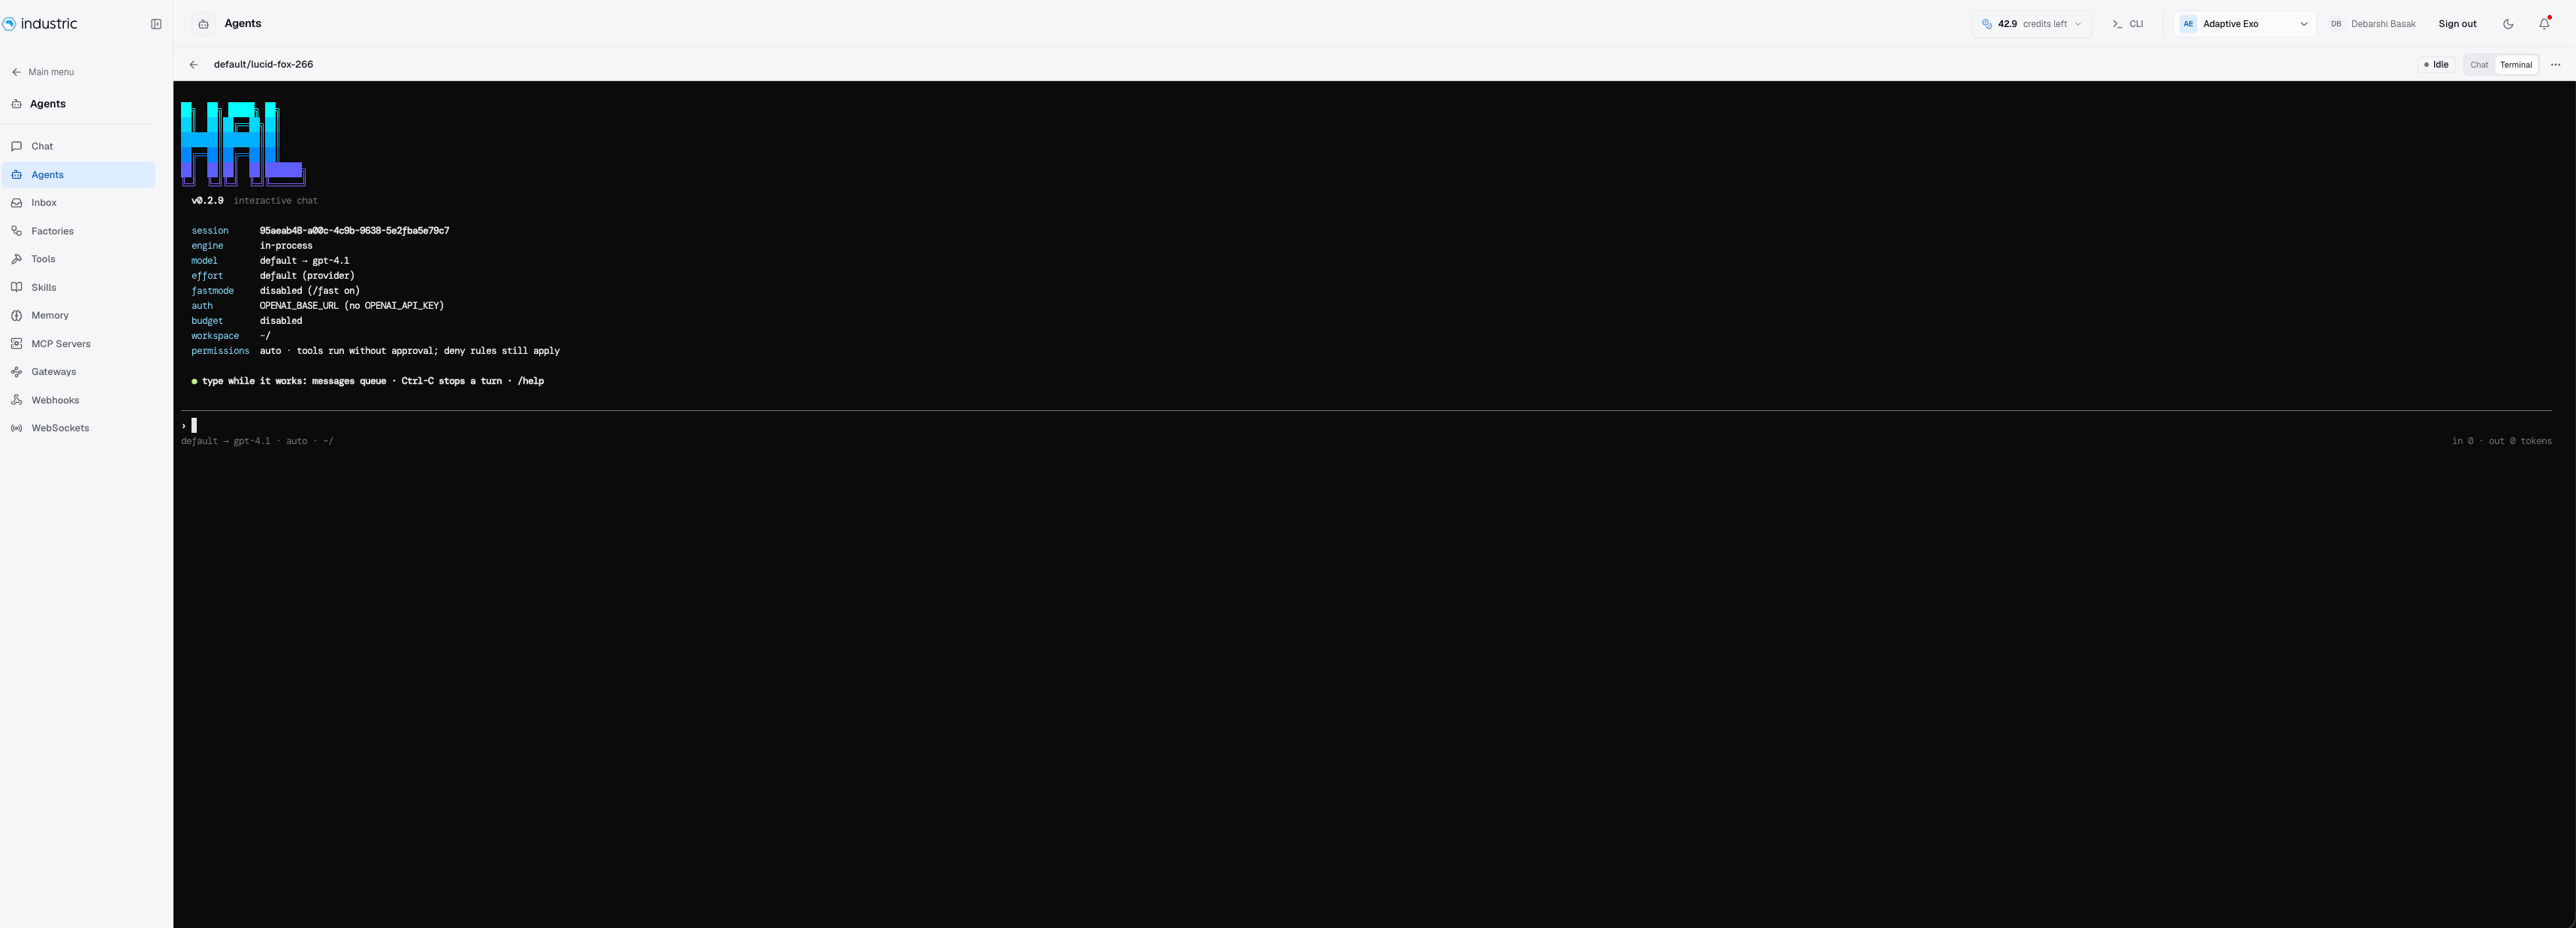
Open Agents in the Platform and click the agent you just created. In the sidebar, select Open terminal.
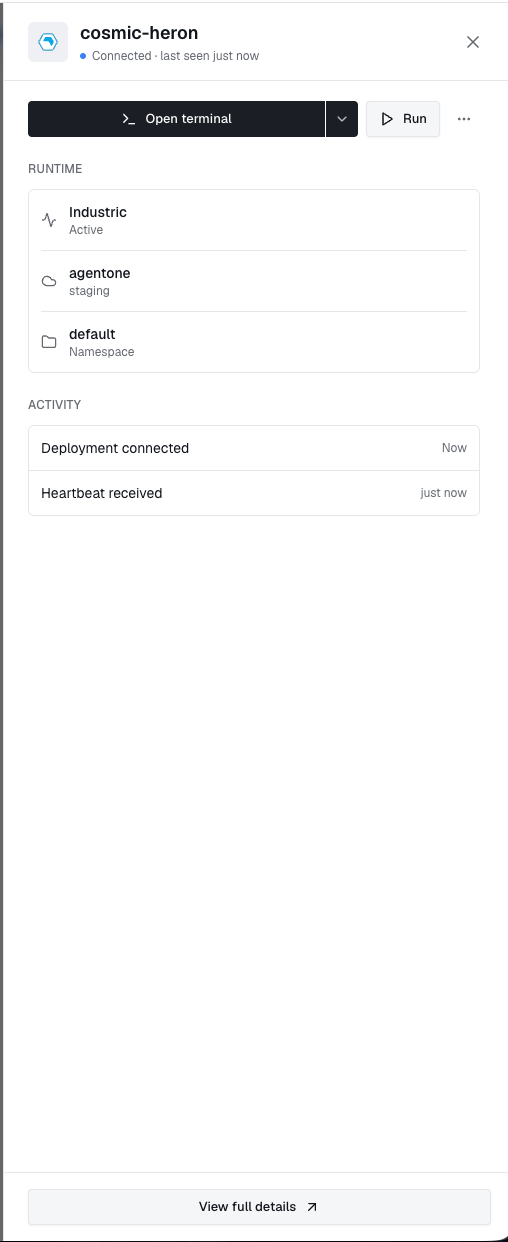
The terminal opens with your agent's configured runtime. Type a message to start working with the agent.
Using CLI
5. Log in to the platform
Sign in to the CLI to run the agent from your terminal. Already signed in from Getting started? Skip ahead.
On managed service the endpoint defaults to https://exo.adaptive.live, so just run exo login — no --endpoint needed:
exo login
exo whoami
To point the CLI at your own control plane, pass --endpoint:
exo login --endpoint https://exo.example.com
exo whoami
6. Start a CLI session
List your agents to confirm it's there, then fire a session and drop into it to watch and interact with it:
exo agent list
exo agent connect production/adaptive/hello-agent
7. Verify the session
Check that the agent can use the analytics tool and returns the requested signups. Review its output in the terminal or the recorded session; if a tool is missing, check the attachments and access grants.
Next steps
- Add more connections and engine-native permissions with the Tool CRD.
- Read the full Agent CRD reference for every field.